ISO/IEC 42001 is the first international standard for managing artificial intelligence responsibly. Rather than regulating the technology itself, it gives organisations a structured way to govern how AI systems are developed, provided or used, covering risk assessment, impact on people and society, and accountability throughout the AI system’s life cycle.
Certification / Accreditation
ISO 42001 AI management systems
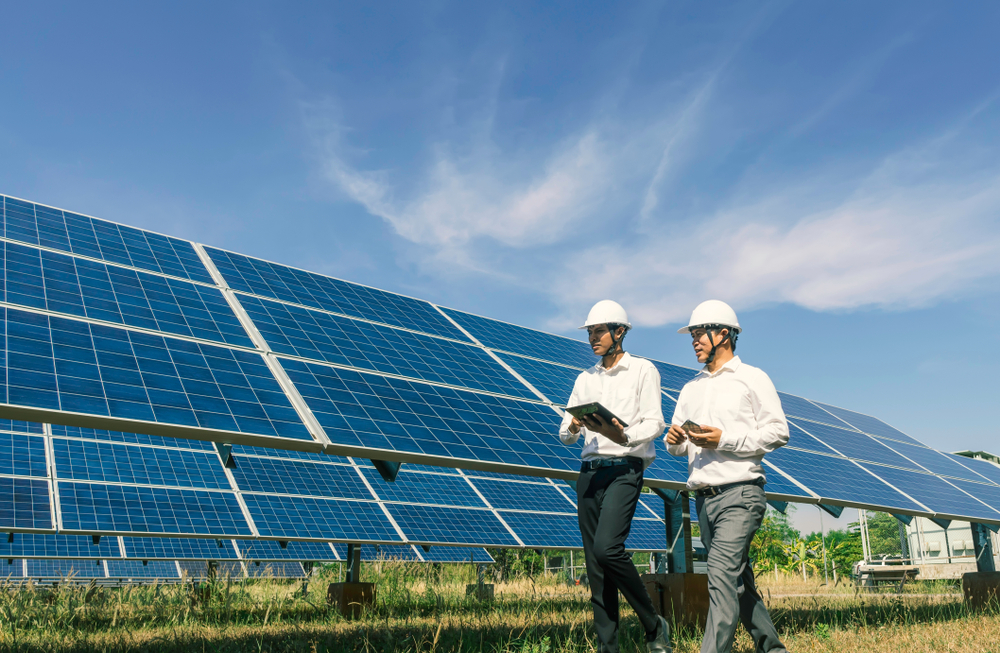
At its core, it asks you to understand your role in relation to AI, whether as a provider, developer, deployer or user, and to build oversight proportionate to that role. Published in December 2023, it is a first edition standard with no revision yet announced.
Who it’s for and what’s involved
Relevant if you are:
Achieving certification involves:
How Q! supports certification
Governance for a technology that’s still moving
AI management is new territory for most consultancies as much as for clients. We translate ISO 42001’s risk and impact assessment requirements into something a non-technical board can actually govern, rather than a checklist bolted onto an existing QMS. Where you already hold ISO 9001 or ISO 27001, we build on the shared structure rather than starting again.
Your first AI governance framework, built on what you already have, not from scratch.
Mini FAQs
It depends more on how mature your governance is than on the technology itself. The standard does not ask you to understand the inner workings of a model, it asks you to demonstrate that someone is accountable for the risks and impacts of using or providing it. Organisations that already have a management system in place, ISO 9001 or ISO 27001 for instance, tend to find the structure familiar even if the subject matter is new.
Yes, if those tools are material to how you deliver services to customers. The standard applies to AI providers and AI users alike, and the requirements scale to your role. A business using AI tools internally has a lighter set of obligations than one developing or selling an AI product, but both fall within scope.
ISO 42001 is not a legal requirement anywhere, but it gives you a ready-made governance structure that maps closely onto what regulators are starting to ask for, including risk classification and impact assessment under the EU AI Act. Certifying now puts you ahead of regulation rather than scrambling to build a framework once it lands.
Yes. ISO 42001 follows the same Harmonised Structure as ISO 9001, ISO 27001 and ISO 14001, so if you already hold one of these, integration is straightforward rather than a parallel system. Many organisations build their AI governance on top of an existing ISO 27001 information security system, since the two overlap significantly on risk and data handling.
More people than you’d expect. Because the standard asks you to assess impacts on individuals and society, not just technical risk, it pulls in people beyond IT: legal, HR, and whoever owns customer relationships, since they’re often the ones who can see how an AI system actually affects people in practice.
Relevant case studies
We’re proud of the service we provide and the feedback we get from our clients. but don’t just take our word for it.
Client: QFactorial
Our own B Corp journey: practising what we preach
Read moreWhatever business stage you are at…
We’re
here.